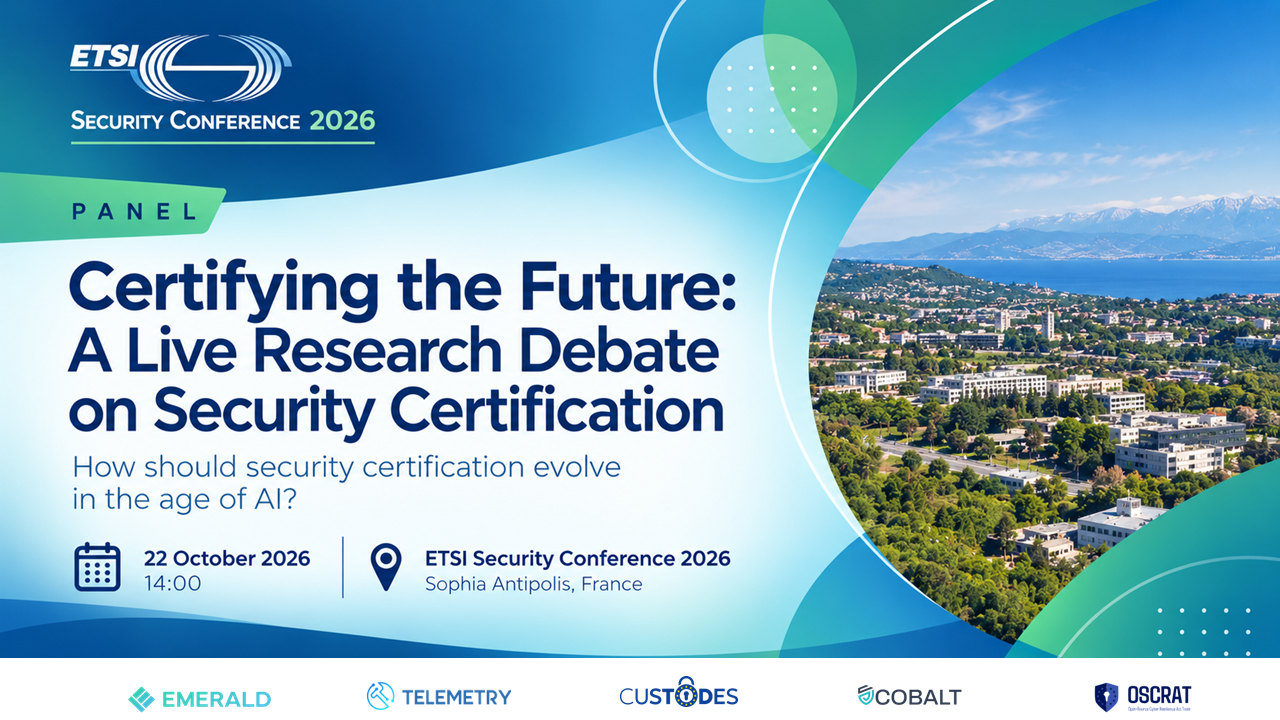
On 22 October 2026, representatives from five European cybersecurity research projects came
together at the ETSI Security Conference 2026 in Sophia Antipolis, France, for an interactive panel
entitled “Certifying the Future: A Live Research Debate on Security Certification”.
The panel brought together EMERALD, TELEMETRY, CUSTODES, COBALT and OSCRAT, all members of
the European Cluster for Cybersecurity Certification (EC3), to exchange perspectives on the evolution
of cybersecurity certification in an increasingly complex technological landscape.
Moderated by Björn Fanta (Fabasoft), with the participation of Martin Gilje Jaatun (SINTEF) and
Yiannis Koufos (Demokritos), the discussion addressed a central question: How should security
certification evolve in the age of Artificial Intelligence?
Towards the Next Generation of Cybersecurity Certification
As digital infrastructures become increasingly interconnected and technologies such as Artificial
Intelligence introduce new security challenges, traditional certification approaches face growing
pressure to evolve.
The need for more efficient, adaptable and scalable certification processes has become particularly
relevant in the context of cloud services, IoT ecosystems and other complex digital environments. At
the same time, ensuring interoperability between different certification approaches and aligning
technical developments with evolving regulatory and standardisation requirements remain important
challenges.
Against this background, the ETSI panel provided an opportunity to bring together complementary
research perspectives and examine how European innovation initiatives are addressing these
challenges.
Rather than presenting individual project achievements in isolation, the discussion aimed to explore
where the different approaches converge, where they diverge, and what lessons can be drawn from
their complementary perspectives.
Different Perspectives on the Future of Cybersecurity Certification
The five participating projects — EMERALD, TELEMETRY, CUSTODES, COBALT and OSCRAT — address
cybersecurity certification from different technological and methodological perspectives. Although
their research activities focus on different challenges and application domains, they share the ambition
of making certification processes more efficient, adaptable and responsive to evolving security
requirements.
The TELEMETRY project has focused on how its testing and monitoring tools can contribute to
satisfying the requirements of specific provisions of ETSI EN 303 645. For instance, Provision 5.13-1B
“Data input […] shall be validated by the device regarding unexpected data input […]” is addressed in
TELEMETRY through a fuzzing tool with a purpose-built fuzzing harness. This is a probabilistic approach
that does not constitute exhaustive testing. Provision 5.2-3 “Manufacturers should continually monitor
for, identify and rectify security vulnerabilities […]” is addressed through the TELEMETRY SBOM tool,
which enables periodic checks against the National Vulnerability Database (NVD) for any newly
discovered vulnerabilities in the components listed in the SBOM. The SBOM tool is combined with the
Spyderisk tool for ranking vulnerabilities to address Provision 5.3-8 “Security updates shall be timely”,
ensuring that the most important vulnerabilities can be addressed first.
Automation, Continuous Assessment and Emerging Technologies
One of the key challenges in cybersecurity certification is the need to move beyond resource-intensive,
point-in-time assessments towards more continuous and automated approaches.
The future of cybersecurity certification increasingly depends on continuous, evidence-based
security assurance throughout the supply chain. As vulnerabilities emerge, components are updated
and system configurations change, research initiatives such as those represented in the panel are
exploring how automated evidence collection, continuous monitoring and advanced assessment
techniques can identify security-relevant changes, trigger targeted reassessments and maintain up-to-
date security information across stakeholders. These capabilities can support more efficient
certification processes by reducing duplicated assessment efforts and enabling the reuse of security
evidence. This approach is explored by projects such as DOSS, a member of the EC3 Cluster, which
integrates automated component testing, system-level security modelling, compliance assessment
and secure device deployment through a common architecture, using the Device Security Passport to
facilitate structured security information exchange throughout the supply chain.
Emerging technologies, particularly Artificial Intelligence and Digital Twins, can further advance this
approach by automating complex analyses, supporting the interpretation of security requirements,
and enabling simulation-based assessments. When combined with machine-readable security
evidence, these technologies can make assessments more efficient, repeatable, and scalable, while
retaining expert oversight for results that require human judgement.
These developments could help certification and conformity assessment processes rely on more
current and reusable evidence, reducing repeated manual evaluations and supporting lifecycle cybersecurity management in line with evolving European regulatory requirements, including the
Cyber Resilience Act.
Finding Common Ground: Convergence and Divergence
The projects did not discuss their overall objectives, but rather how they each promote automated
auditing and compliance mechanisms and frameworks, moving away from one-time, paper-based
audits toward ongoing, automated checks. In most projects’ approaches, tools automatically gather
evidence demonstrating compliance with specific security requirements. For instance, TELEMETRY
links its testing and software tracking (SBOM) tools to the ETSI EN 303 645 standard, while COBALT
uses the OSCAL format to connect measurements directly to specific risks and security controls.
Detailed inventories (Bills of Materials) for software, encryption, and services are common tools across
projects.
Differences mainly involved the targets of evaluation and the limitations of automation. The projects
cover different environments, including connected devices, cloud services and AI systems, and address
different regulatory and certification frameworks, such as ETSI EN 303 645, EUCS and the Cyber
Resilience Act. AI plays a dual role as it can help automate testing, but AI systems also need to be
assessed and certified. However, AI-specific threats (such as data tampering, adversarial attacks and
model theft) still lack standard rules. Furthermore, automated testing cannot address every aspect of
compliance, thus the assessment of organisational policies still requires human judgement. The main
shared challenge is the lack of common formats for test results.
Key Insights from the Panel
While experts anticipate the emergence of trustworthy AI within the next five years, they emphasized
that the results produced by automated systems cannot yet be blindly trusted. Consequently, the
future of cybersecurity certification lies in integrating AI capabilities into certification frameworks,
leveraging a strategic combination of general-purpose Large Language Models (LLMs) and specialised
models while maintaining human oversight as a central element of the process.
Looking Ahead: Strengthening Collaboration through EC3
Beyond the technical discussion, the panel highlighted the importance of collaboration among
European research initiatives addressing cybersecurity certification. The European Cluster for
Cybersecurity Certification (EC3) provides a forum for exchanging knowledge, identifying synergies
and exploring opportunities to bring complementary research results together.
By connecting projects working across different technological domains and certification approaches,
EC3 strengthens cooperation within the European cybersecurity research community and supports the
development of next-generation agile certification solutions.
Continuing the Dialogue on Cybersecurity Certification
The panel “Certifying the Future: A Live Research Debate on Security Certification” brought together
different research perspectives at the ETSI Security Conference 2026, highlighting the importance of
continued dialogue and collaboration. Through the exchange of experiences, approaches and ideas,
the discussion provided an opportunity to reflect on shared challenges and explore how joint efforts
among European research initiatives can support the evolution of certification practices.
The insights gathered during the panel will contribute to the broader exchange of knowledge within
EC3 and the European cybersecurity certification community.
Further information: https://www.etsi.org/events/2645-etsi-security-conference-oct2026/