Four real-world pilot audits confirmed that EMERALD can turn cloud compliance from a manual, point-in-time task into a structured, evidence-driven process. The feedback is already shaping the next version of the tool.
Between 23 September and 7 October 2026, lead and technical auditors from DNV Cyber ran four pilot audits of the EMERALD Compliance-as-a-Service framework with the project’s audit partners:
- IONOS (IaaS)
- CloudFerro (IaaS/PaaS)
- Fabasoft (SaaS)
- CaixaBank with OpenNebula (hybrid multi-cloud)
The audits covered BSI C5, EUCS and a custom scheme for the finance industry, based on ISO/IEC 27001, ENS, DORA, NIST and CIS.
Faster, repeatable internal audit preparation
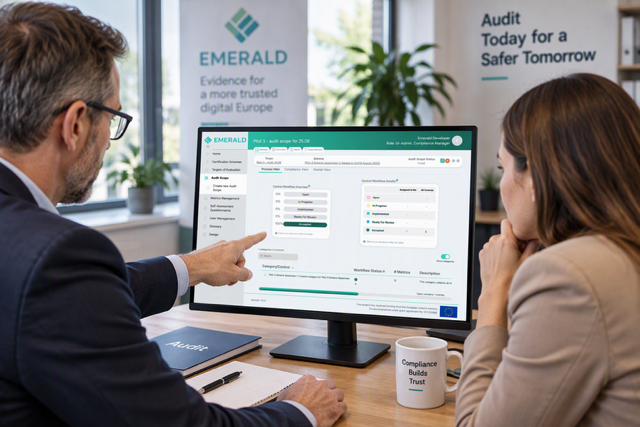
For compliance managers preparing internal audits, EMERALD turns audit preparation into a structured, repeatable workflow. It automatically collects evidence from cloud APIs and policy documents, keeps it in a tamper-protected Evidence Store, and maps it to controls and metrics. Compliance managers can quickly create different views (audit scopes) to the stored evidence according to different internal audit needs.
Visibility into third-party cloud providers
For organisations that depend on third-party cloud service providers, the CaixaBank pilot showed EMERALD assessing their suppliers IONOS and CloudFerro resources alongside the bank’s own infrastructure. This gives a regulated financial institution a practical way to check that its suppliers meet legal and regulatory requirements.
Trustworthy evidence for external attestation
For external audits and attestation reports, such as the independent attestation required under BSI C5, EMERALD gives auditors trustworthy, traceable view to evidence while sensitive information stays under the provider’s control. The audit preparation and evidence presentation to auditors is supported by a central flexible workflow combining requirements, resources and evidence. The audit sessions can focus only on unclear evidence shortening auditors time and effort onsite and meetings.
Results across the pilots
In the Fabasoft audit, the auditors agreed with every result the EMERALD tool produced. In the IONOS audit, the cloud API could not yet supply all the information the generic metrics asked for, so further refinement is planned. In the Cloudferro audit, the availability of suitable available metrics reduced the audit scope and control coverage. In the CaixaBank case, most of the controls and metrics worked as intended after corrections based on the auditor’s feedback.
Rapid improvement driven by audit feedback EMERALD matured noticeably during and after the audit period, driven by what the pilots revealed. Later releases fixed many user-interface issues, added clearer metric descriptions and introduced a PDF compliance report.
Looking ahead EMERALD has strong potential to become a key enabler of continuous, evidence-based cloud certification in Europe, including under the upcoming EUCS scheme. The pilot audits identified clear next steps:
- Larger metric libraries
- LLM-based analysis of policy documents
- User-interface views that scale to much larger data sets
Together, these would make audit preparation and execution faster and more reliable.